
One-time org setup
There are seven steps, done once per org. Step 6 is optional. Allow about an hour the first time; most of it is building the signing site. You need the Sliick Docs Admin permission set for all of it.
Step 1: Permission sets
Section titled “Step 1: Permission sets”- Senders need
Sliick Docs UserorSliick Docs Admin. - Admins who configure the steps below need
Sliick Docs Admin. Sliick Docs Signer Guestis for your signing site, not for people. You assign it in Step 2.
Step 2: Build the signing site
Section titled “Step 2: Build the signing site”Signers sign on a public page hosted on an Experience Cloud site in your own org. Salesforce does not let a package include a site, so you build it once yourself. The signing component comes with the package: you put it on a page and tell Sliick Docs where that page is.
-
Create the site. In Setup, go to Digital Experiences, then All Sites, then New. Choose Build Your Own (LWR). Give it a name and a URL path, such as
esign. -
Build the signing page. Open the site in Experience Builder. Add a new standard page, set its route to
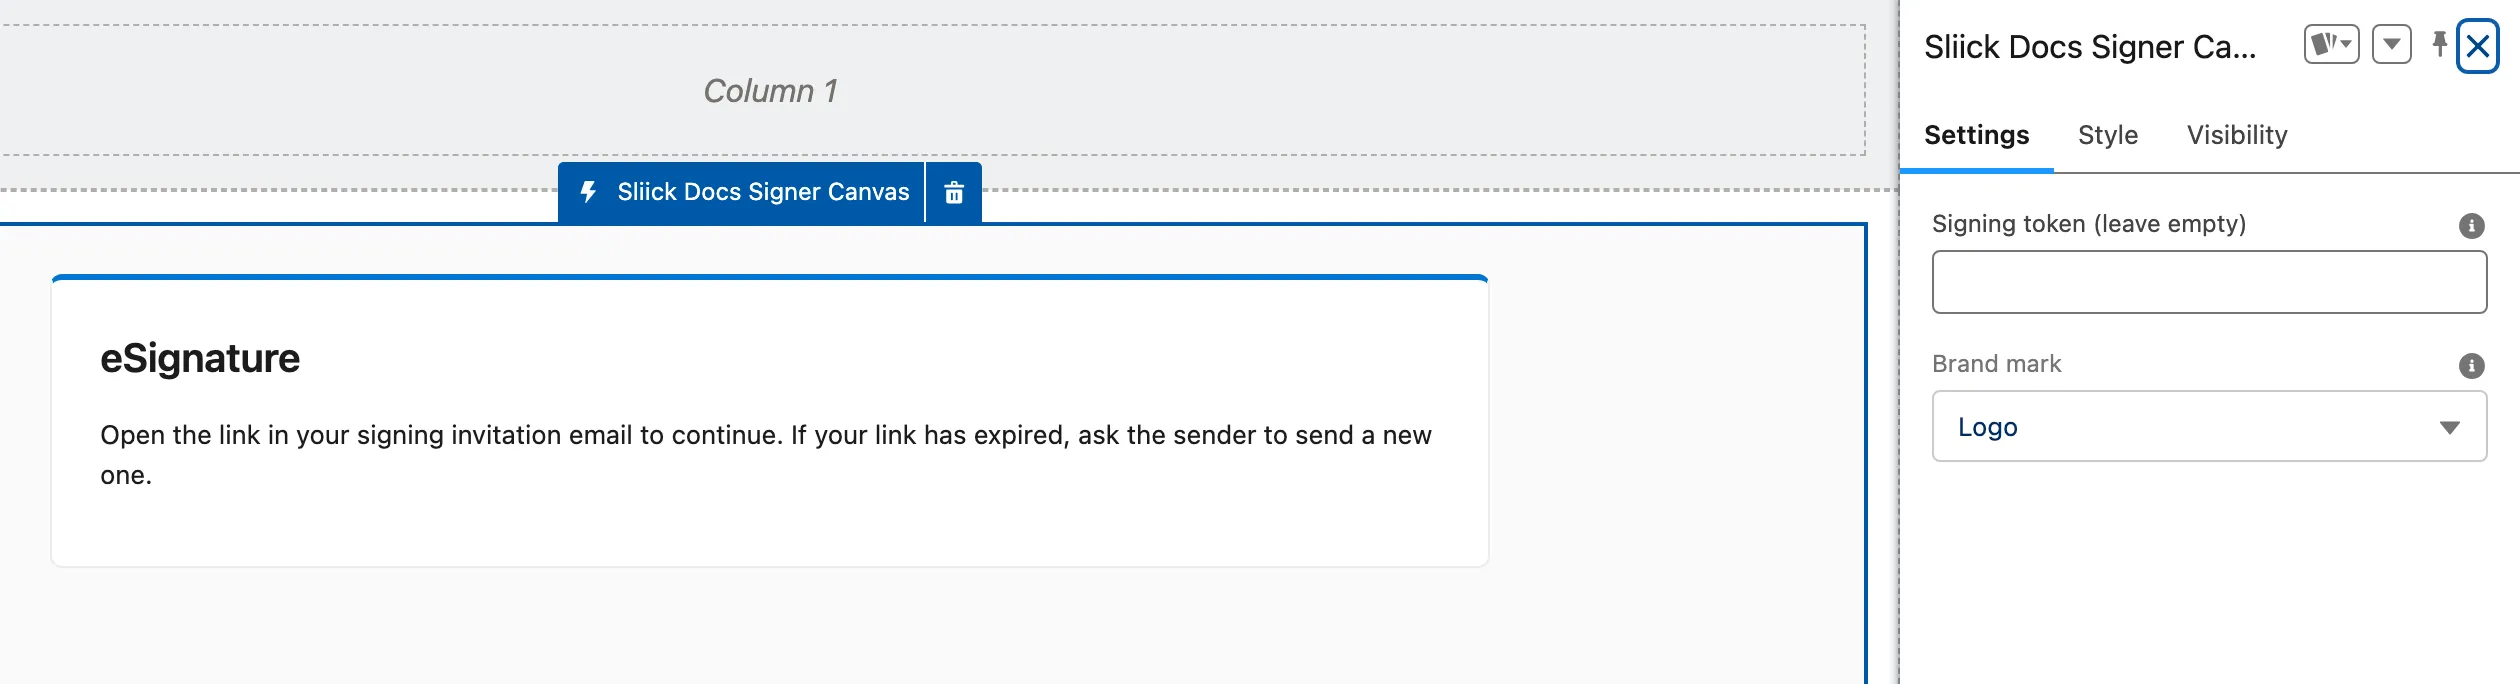
/sign, and drag the Sliick Docs Signer Canvas component onto it. Keep the page public.The component has two properties:
- Signing token (leave empty). Leave this blank. Each signer’s link supplies it. If you type a value here, every visitor sees that one signer’s request. While you work in Experience Builder there is no link, so the page shows eSignature and tells the visitor to use their invitation email. That is expected. Anyone who opens the page without a link sees the same thing.
- Brand mark. Choose None (the default), Logo or Text. Logo shows the e-signature logo from Settings. Text shows your brand name in words. The accent colour always comes from your e-signature branding, so the page matches the invitation email. You set this per page, so the signing page and the verification page can differ.
-
Turn on guest file access. In Experience Workspaces, go to Administration, then Preferences, and turn on guest access to files and records. Without it, the signing page loads but the document never appears. Salesforce changes the exact wording of this checkbox between releases; look for the guest access setting for files and records.
-
Publish and activate. Publish in Experience Builder. Then, under Administration, activate the site so its status is Live.
-
Assign the signer permission set. In the site’s Administration, open Guest User Profile, then View Users. Open the user listed and add the
Sliick Docs Signer Guestpermission set. Assign the permission set itself, not a permission set group: Salesforce does not allow groups here.
Step 3: Tell Sliick Docs where the site is, and choose a from address
Section titled “Step 3: Tell Sliick Docs where the site is, and choose a from address”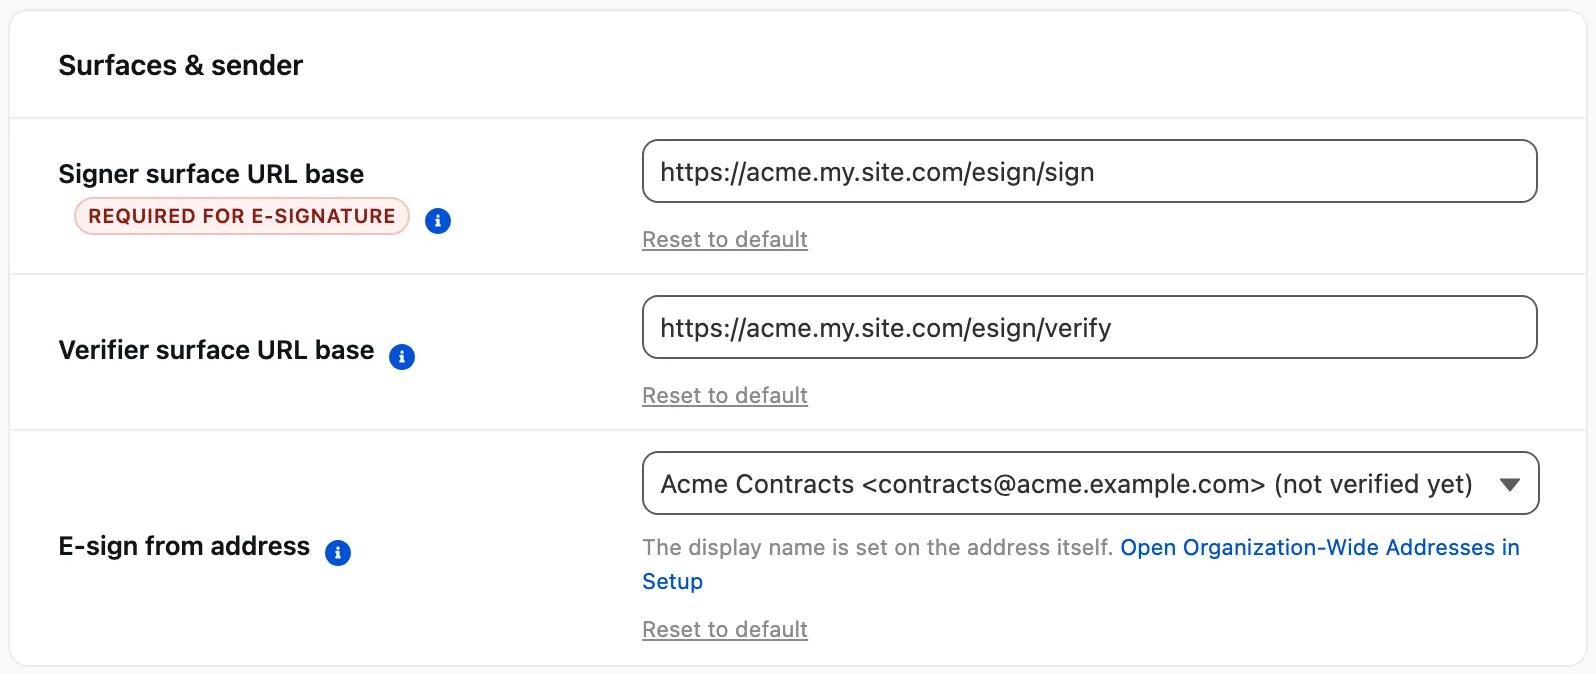
Sliick Docs will not send anything for signature until both of these are set. They are on the E-signature tab of the Sliick Docs Settings page, under Surfaces & sender. Neither has a default. If one is missing, the send is refused with a banner naming it, so a signer is never sent a link that cannot work. You can still create and edit drafts in the meantime.
- Signer surface URL base. The full address of the signing page you just built: the site address plus the route, for example
https://acme.my.site.com/esign/sign. - E-sign from address. In Salesforce Setup, create and verify an Org-Wide Email Address and tick Allow All Profiles on it. Then pick it here. The one-time verification code is sent from your public site, and Salesforce only allows that from an org-wide address open to all profiles. If the address you pick is limited to selected profiles, the setting tells you that is why the check has not passed. An address still waiting for verification is flagged when you send, but does not block the send.
Check who your emails come from. The E-sign from address list shows each address as Display Name <address>, the way it appears in a recipient’s inbox. Once the address is verified, Currently sending as below it shows the address e-signature will actually use. If you have not chosen one, it is marked inherited: Sliick Docs uses the first address alphabetically. So an org with accounts@, noreply@ and support@ addresses sends every signature request from accounts@ unless you change it. It is worth checking even if you are happy with the default.
The display name can only be changed on the address itself in Setup, and the card links you there. If you do not have access to view org-wide addresses, the card says so. Your setting still saves, and e-signature may still be sending perfectly well.
Classic sign of a missing from address: the invitation email arrives, but the verification code never does.
Step 4: Schedule the nightly integrity check
Section titled “Step 4: Schedule the nightly integrity check”Do this once, as a user with Sliick Docs Admin. In Setup, open the Developer Console, choose Debug, then Open Execute Anonymous Window, and run:
sliick.DocSignChainVerifier.scheduleNightly();Every night, this checks that each signature request’s history and its stored documents are unchanged since they were recorded. If anything fails, you get a Salesforce notification. If everything passes, it stays quiet, so no news is good news.
You can also run the check yourself at any time. See Verification and certificates.
Retention needs nothing extra. It runs with the document retention sweep you already have.
Step 5: Add the components to your record pages
Section titled “Step 5: Add the components to your record pages”In Lightning App Builder:
- Add Sliick Signatures to the record pages you send from, such as opportunities or accounts. Senders start and manage requests here.
- Add Sliick eSignatures - Signed Documents to the Doc Signature Request record page, so senders can download the certificate and signed documents from the request itself.
Step 6 (optional): Publish the public verification page
Section titled “Step 6 (optional): Publish the public verification page”To let counterparties check signed documents themselves, add the Sliick Docs - Document Verifier component to a published page on an Experience site. Then set Verifier surface URL base in Settings, under Surfaces & sender.
Anyone with a signed PDF can then check it on that page, with no login. The file is checked in their own browser and is never uploaded.
This component has the same Brand mark property as the signing page: None (the default), Logo or Text, with the accent colour from your e-signature branding.
Step 7: Turn e-signature on for a template
Section titled “Step 7: Turn e-signature on for a template”E-signature is off on every template until someone with Sliick Docs Admin or Sliick Docs Template Author turns it on, from the E-sign tab in the Template Editor’s right-hand panel.
Turning it on shows a warning about the kinds of documents that are excluded from, or restricted for, electronic signing. Sliick Docs records who acknowledged it and when, and copies that onto every request sent from the template. If the warning is updated later, templates acknowledged against the older version ask to be acknowledged again. To use your own warning wording, see Consent and sender wording.
On the same tab you set up signer roles and place the fields each role fills in. Roles are placeholders: real people are matched to them when you send, and a role linked to a record field fills itself in. The full walkthrough is in Setting up a template for signature.
Sending an existing or uploaded PDF needs no template. The sender ticks an acknowledgment that they are authorised to send the document on every send, and the request cannot be sent without it. For a PDF that did not come from a template, that tick is the authorisation on record.
After every upgrade: republish the signing site
Section titled “After every upgrade: republish the signing site”After every upgrade, republish your signing site before you send anything. An Experience site keeps showing the version of the page it was last published with. Until you republish, signers see the signing page from your previous release.
This matters. An out-of-date signing page can tell a signer something untrue, for example that a verification code has been sent when it could not be emailed. It can also miss details the certificate needs, such as the signer’s location. A Certificate of Completion cannot be reissued, so a request signed on an out-of-date page keeps those gaps for good.
Republish first, then send. If a signer still sees the old page afterwards, ask them to reload it, because their browser may have kept an old copy. The signature itself completes either way.