
Verification and certificates
After a document is signed, there are three ways to show it was signed properly and has not been changed since:
- Integrity checks in your org, run every night and whenever you ask.
- The Certificate of Completion, which records how the signature was collected.
- The public verification page, where anyone holding the signed PDF can check it, without access to your org.
Checking your records on demand
Section titled “Checking your records on demand”Every night, Sliick Docs checks that each request’s history and its signed documents are unchanged since they were recorded. It only tells you if something fails. (An admin sets this up once: see One-time org setup.)
To check now, for example while dealing with a dispute:
- Open the Diagnostics tab.
- On the Signature integrity card, choose Verify signature integrity.
- The check runs in the background. Stay on the page and the result appears on the card.
You get two results:
- Signature records: the history of each request, from sending to signing.
- Signed documents: the stored signed files.
Each shows No issues found or Issues found - check alerts, a short summary including how many items were checked, a Last verified date, and who ran it. Before anyone has run it, it shows Not verified yet.
The check covers only the records you have access to, so look at how many were checked. If the count is 0, you could not see anything to check, and No issues found does not mean everything is fine. If you cannot see signature records at all, the card is not shown.
What the Certificate of Completion records
Section titled “What the Certificate of Completion records”The certificate is what you give anyone who asks how a signature was collected. It records:
- Who and when: the sender, every signer, and when each one signed.
- Where each signature was made from.
- Each signer’s consent wording. The exact consent text the signer accepted, its version, and when they accepted it. This is fixed when the signer is invited, so changing your consent wording later does not change it.
- The full history of the request, with a summary at the top. The summary and the detailed list describe the same events, so a reader can check one against the other.
- Names as they are written. Names in Chinese, Japanese or Korean print in their own script.
A certificate is never issued for a request whose records fail the integrity check. A certificate backed by records that do not check out would be worse than none.
Downloading needs verification. A signer must enter their verification code before they can download the signed document, the completed package or the certificate. If you reset a signer’s verification after completion, they are asked to verify again rather than turned away.
Matching a page to its request. Every signed page carries a short reference code in the header and margin. The same code is on the certificate and in the emails, so anyone can match a printed or forwarded page back to the request it came from.
Public verification
Section titled “Public verification”If your admin published the verification page during org setup, anyone holding a signed PDF can check it themselves. They need no login, no Salesforce account and no access to your org.
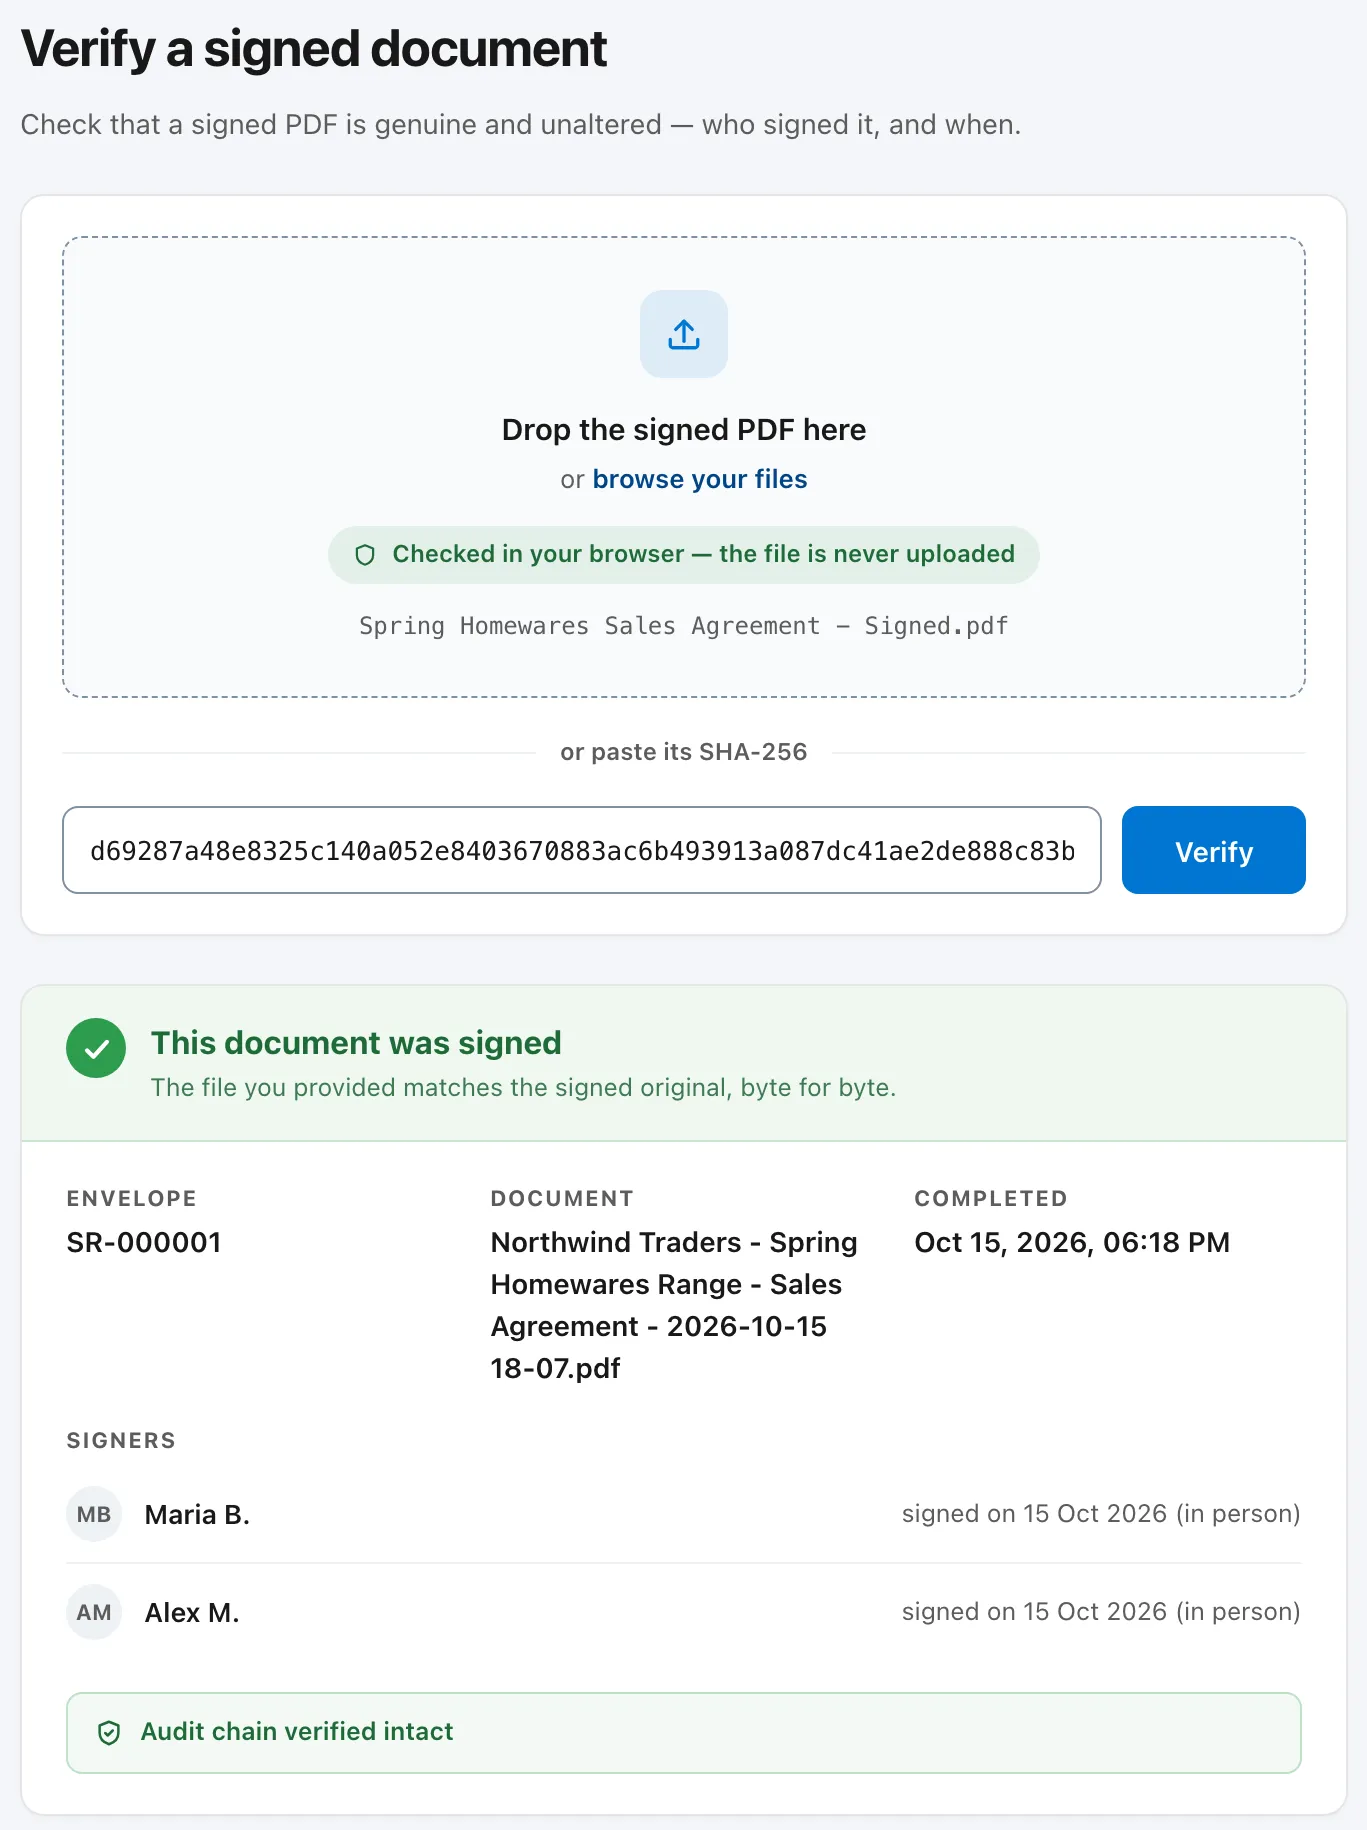
On the Verify a signed document page, they:
- Drop the signed PDF onto the page, or choose browse your files. (If they have the document’s SHA-256 code, they can paste that instead.)
- Wait a moment while the file is checked. It is checked in their own browser and is never uploaded.
What they see if it matches: This document was signed, with “The file you provided matches the signed original, byte for byte.” Below that is the request, the document name, the completion date, and the signers’ names with personal details partly hidden. It also shows Audit chain verified intact, meaning the request’s history in your org passed its integrity check. If that history could not be checked, it says Audit chain could not be confirmed instead.
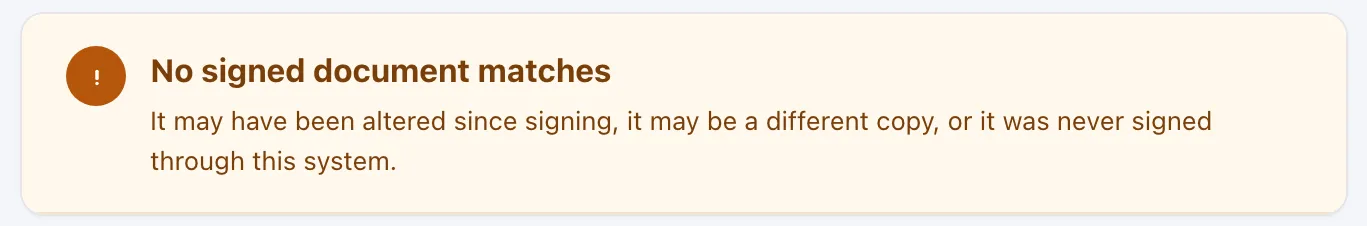
What they see if it does not match: No signed document matches. The page explains that the file may have been changed since signing, may be a different copy, or was never signed through your org.
What this proves, and what it does not. A match means the file is exactly the one that was signed: any change to the file, however small, stops it matching. It does not check a printed or scanned copy, because that is no longer the same file. For a paper copy, use the reference code on each page instead.
In a PDF reader. If your org uses one of the certified seal tiers, the signed PDF also opens as certified and unaltered in standard PDF readers such as Adobe Acrobat, with no need for this page. The default tier has no seal on the PDF itself, so PDF readers show no signature status. See Signing tiers.
The page reads only a limited public summary of each completed request, with personal details partly hidden. No private signing details are shown.
This is worth telling counterparties about. When someone asks for a “properly signed” document, this is often what they really want: a way to satisfy themselves that the document in their hands is the one that was signed.